A fake CEO, a fake vendor thread and a real payment queue: inside the layered invoice lure
A September campaign combined executive display names, vendor branding, fabricated history and a near-$50,000 ACH request.
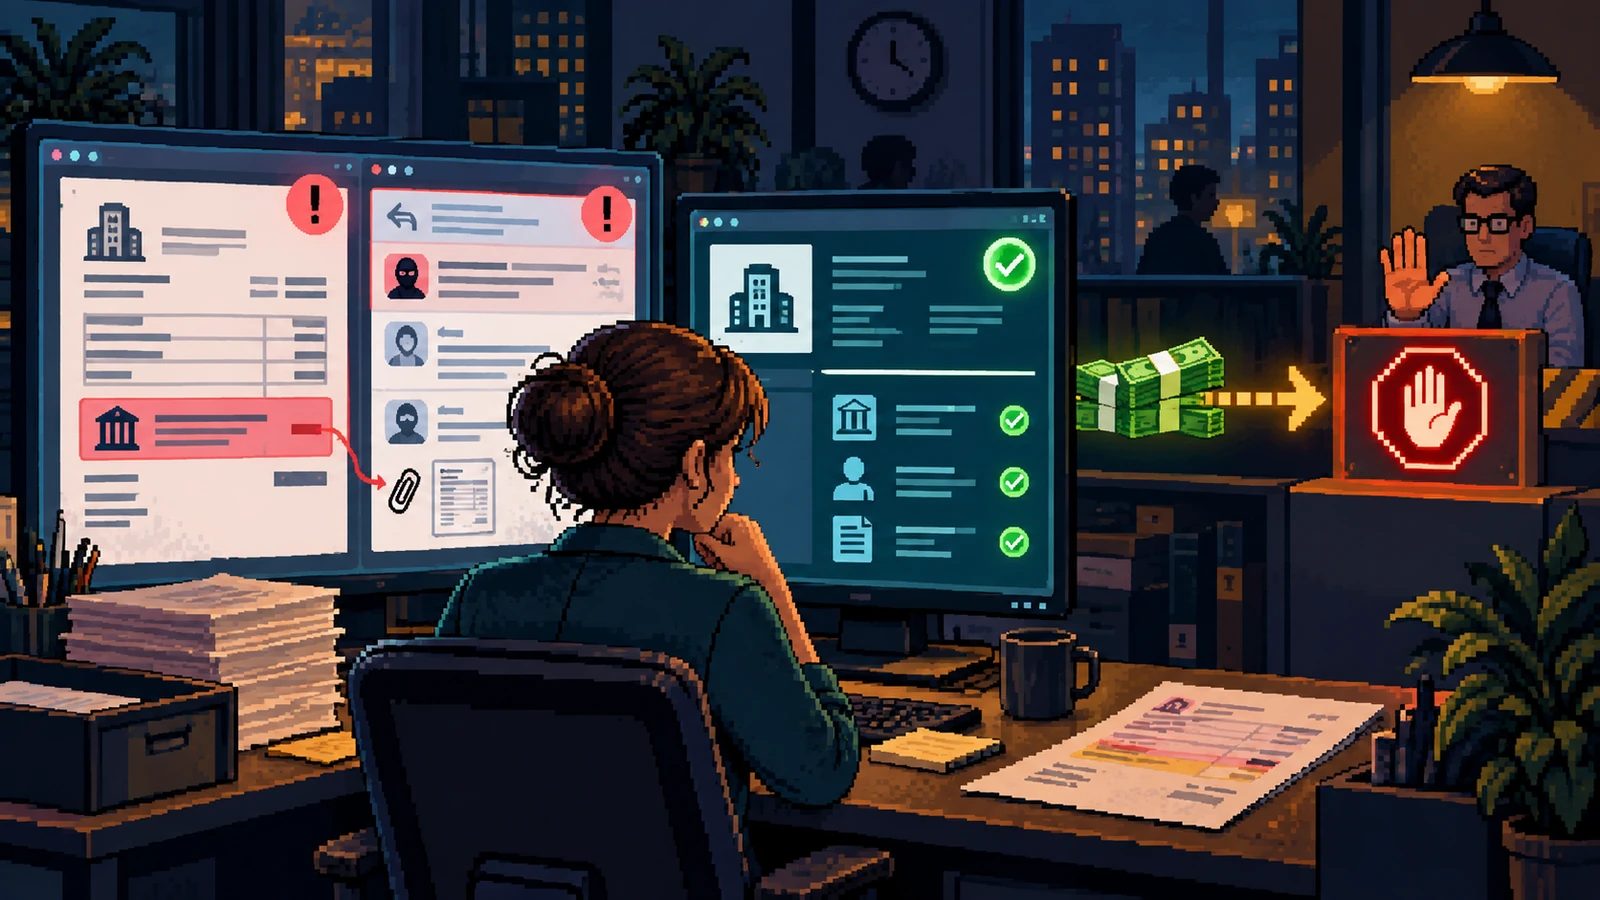
Invoice fraud is often described as one bad email. Microsoft’s September report shows a more persuasive construction: a message appearing to come from a company executive, a professional invoice carrying a familiar vendor’s branding, and a fabricated forwarded conversation that seems to prove earlier approval. The observed request sought an ACH payment of nearly $50,000.
The campaign reportedly sent more than a million messages between August 3 and 5, with most directed at recipients in the United States. Microsoft found no evidence that the legitimate organizations referenced in the lure were compromised. Their names, executives and visual identity were credibility material assembled on attacker-controlled infrastructure.
What Microsoft Security Research, September 10, 2026 actually reported
The actor impersonated CEOs, CFOs or presidents in display names, reply-to fields and signatures; registered lookalike domains; built detailed invoices; and inserted a fake executive-to-vendor exchange below the current request. Microsoft observed indicators consistent with generative-AI-assisted template development, but carefully framed those as indicators rather than proof of how much content AI produced.
A recipient can be technically alert and still be vulnerable to organizational context. The message anticipates the questions a finance employee might ask—who approved this, what was purchased, why the amount is due—and supplies answers inside the same untrusted object. That is precisely why verification must leave the thread.
Borrowed authority
The sender presents as an executive who can approve exceptions.
Borrowed history
A fabricated thread makes the purchase look discussed and settled.
Borrowed brand
A vendor-like invoice and domain provide visual familiarity.
From “Executive approval” to “ACH instruction”
A forwarded thread is part of the claim. It is not independent confirmation of the claim.
Each layer removes a reason to pause. A strong payment workflow deliberately restores that friction before money moves.
| Moment | What it appears to mean | What to verify |
|---|---|---|
| Executive approval | Leadership has already decided | Does the approval exist in the established procurement system? |
| Vendor invoice | The amount and line items are documented | Do vendor master data and bank details match the known record? |
| Forwarded thread | Earlier participants confirmed the purchase | Can either participant confirm through a new internal message or call? |
| ACH instruction | Routine settlement | Did any destination or payment method change? |
How to interrupt ach instruction
The goal is not to teach every accounts-payable employee to investigate domains like an analyst. It is to make unusual payments depend on a second, separate record.
- Pause any new, urgent or changed payment instruction even when the message cites an executive.
- Open the procurement or vendor system separately and compare the purchase order, invoice and bank details.
- Confirm with the approver through a new internal message or known phone number, not Reply.
- Call the vendor using contact information already stored in the vendor record.
- Require dual approval for bank-detail changes and payments outside the normal pattern.
- Report the entire message, including headers and attachment, to security and finance leadership.
Recovery after ach instruction
Once an ACH instruction has been sent, minutes matter. Investigation can continue after the bank has been asked to stop or recall the transfer.
- Contact the financial institution’s fraud team immediately and request a hold or recall.
- Notify the verified executive and vendor without using addresses from the suspicious thread.
- Preserve the email, headers, invoice, domains, payment destination and approval records.
- Review adjacent invoices and mailboxes for similar requests or compromised rules.
- Report the incident through the organization’s legal and law-enforcement process.
Why “Executive approval” can feel routine
In the sequence documented by Microsoft Security Research, September 10, 2026, the story begins with context the recipient can recognize. It continues by explaining away normal friction. It succeeds only when the recipient completes the high-impact action. None of those stages requires carelessness. The approach behind “A fake CEO, a fake vendor thread and a real payment queue: inside the layered invoice lure” works by making the next action appear consistent with the role, project or relationship already in front of the recipient.
Training often overemphasizes spelling mistakes and theatrical urgency. In this case, the stronger question is whether the process has been quietly redesigned around the new contact. “Executive approval” may look routine, yet it can position “ACH instruction” as the natural conclusion. A legitimate request should remain valid after a pause, a call-back and review by another authorized person.
Four decision points before “ACH instruction”
1. Executive approval
Why it works: Leadership has already decided. In a busy day, that explanation can be enough to keep the interaction moving. The safer test is narrower: Does the approval exist in the established procurement system? This does not require the recipient to prove fraud. It only requires the sender’s claim to survive contact with a record or channel that the sender did not create.
What to notice after executive approval: Observe what changes at this point in “A fake CEO, a fake vendor thread and a real payment queue: inside the layered invoice lure.” Does the sender gain a reply, a session, a payment instruction, a new device, a document, or permission to continue? Naming the capability behind leadership has already decided is more useful than guessing the sender’s personality. It gives a colleague or incident team a concrete fact to verify instead of a vague feeling that this particular message looked wrong.
2. Vendor invoice
Why it works: The amount and line items are documented. In a busy day, that explanation can be enough to keep the interaction moving. The safer test is narrower: Do vendor master data and bank details match the known record? This does not require the recipient to prove fraud. It only requires the sender’s claim to survive contact with a record or channel that the sender did not create.
What to notice after vendor invoice: Observe what changes at this point in “A fake CEO, a fake vendor thread and a real payment queue: inside the layered invoice lure.” Does the sender gain a reply, a session, a payment instruction, a new device, a document, or permission to continue? Naming the capability behind the amount and line items are documented is more useful than guessing the sender’s personality. It gives a colleague or incident team a concrete fact to verify instead of a vague feeling that this particular message looked wrong.
3. Forwarded thread
Why it works: Earlier participants confirmed the purchase. In a busy day, that explanation can be enough to keep the interaction moving. The safer test is narrower: Can either participant confirm through a new internal message or call? This does not require the recipient to prove fraud. It only requires the sender’s claim to survive contact with a record or channel that the sender did not create.
What to notice after forwarded thread: Observe what changes at this point in “A fake CEO, a fake vendor thread and a real payment queue: inside the layered invoice lure.” Does the sender gain a reply, a session, a payment instruction, a new device, a document, or permission to continue? Naming the capability behind earlier participants confirmed the purchase is more useful than guessing the sender’s personality. It gives a colleague or incident team a concrete fact to verify instead of a vague feeling that this particular message looked wrong.
4. ACH instruction
Why it works: Routine settlement. In a busy day, that explanation can be enough to keep the interaction moving. The safer test is narrower: Did any destination or payment method change? This does not require the recipient to prove fraud. It only requires the sender’s claim to survive contact with a record or channel that the sender did not create.
What to notice after ach instruction: Observe what changes at this point in “A fake CEO, a fake vendor thread and a real payment queue: inside the layered invoice lure.” Does the sender gain a reply, a session, a payment instruction, a new device, a document, or permission to continue? Naming the capability behind routine settlement is more useful than guessing the sender’s personality. It gives a colleague or incident team a concrete fact to verify instead of a vague feeling that this particular message looked wrong.
Where workplace deception needs protective friction
The first protective move is simple: Pause any new, urgent or changed payment instruction even when the message cites an executive. The second is procedural: Open the procurement or vendor system separately and compare the purchase order, invoice and bank details. Together, those moves separate the sender’s narrative from the organization’s evidence. They are deliberately slower than clicking Reply, but much faster than recovering money, identity access or a compromised device.
The next layer is social. Confirm with the approver through a new internal message or known phone number, not Reply. People bypass controls when they believe delay will disappoint a customer, executive or colleague. A good policy therefore grants explicit permission to pause and defines who owns the follow-up. The recipient should not have to investigate alone while the requester waits on the line.
Evidence to retain after “Executive approval”
Evidence about a fake ceo, a fake vendor thread and a real payment queue: inside the layered invoice lure is most useful when it captures the original route and the requested action. Do not keep chatting simply to make the sender confess. Save what already exists, note what was approved or disclosed, and move reporting to a trusted channel. The following details give responders a workable starting point:
- Contact the financial institution’s fraud team immediately and request a hold or recall
- Notify the verified executive and vendor without using addresses from the suspicious thread
- Preserve the email, headers, invoice, domains, payment destination and approval records
- Review adjacent invoices and mailboxes for similar requests or compromised rules
A screenshot can communicate the visible story around executive approval, but the original message, full sender address, link, meeting invitation or transaction reference may contain more useful technical detail. Preserve both when it is safe to do so. Avoid forwarding suspicious material around the organization; use the approved reporting method so the artifact behind ach instruction does not become a second exposure.
A two-minute response before “ACH instruction”
Stop before the highest-impact request: pause any new, urgent or changed payment instruction even when the message cites an executive. Leave the sender’s route, then check the claim in a system or contact record you already trust. If it is genuine, resume through the verified process; if it is not, report the original interaction and warn the people most likely to receive the same workplace deception pretext. That sequence works even when the message is polished or the screen belongs to a legitimate service.
What workplace deception teams should change
Finance teams should test the exception path, not only the normal one. Define which amounts, new destinations and executive requests trigger a callback; record approvals outside email; and make it culturally safe to delay a senior person’s request while verification occurs.
Polish is cheap, and fabricated context is scalable. The durable control is a payment process that cannot be completed using evidence contained entirely within one message.
Microsoft Security Research, September 10, 2026 ↗
Microsoft’s report supplies the campaign volume, payment example and infrastructure findings. The payment controls here are general defensive guidance and should be adapted to each organization’s bank and approval system.