The short device code does not identify whose device you are authorizing
Microsoft detailed a widespread campaign that used AI-personalized business lures to push targets into a legitimate device-code flow.
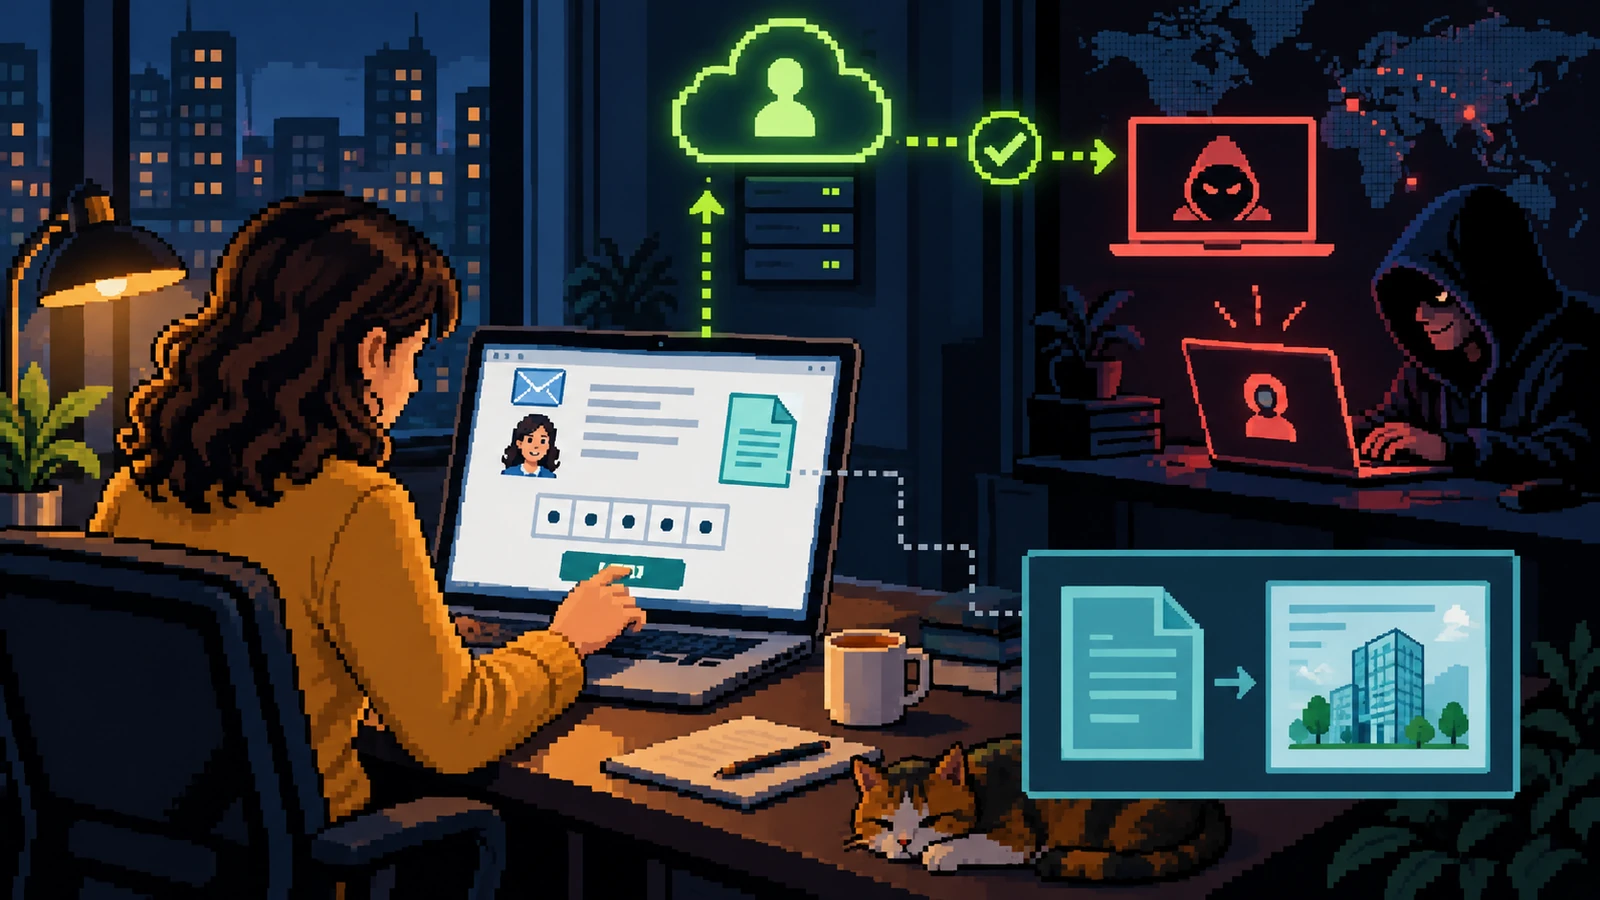
Device-code sign-in exists for devices with limited keyboards, but the person entering the code can accidentally authorize someone else’s session. Microsoft’s campaign used targeted themes such as proposals, invoices and manufacturing workflows, then guided recipients into a legitimate authentication page with an attacker-controlled code.
Because the identity-provider page is real, domain checking alone cannot answer the central question. The code represents a session. If you did not initiate that session on a device in front of you, do not authorize it.
What Microsoft Security Research, April 6, 2026 actually reported
Microsoft Security Research, April 6, 2026 documents a current campaign or warning centered on the short device code does not identify whose device you are authorizing. It describes the observed delivery route, the trust signal being borrowed and the action attackers wanted. We link the record in full so readers can separate reported facts about personalized email from our practical interpretation of cloud access.
Borrowed signal
A relevant proposal or document.
Decision point
Only the document opens.
Defensive reset
Never enter a device code supplied by another person or message.
The audience pain point is uncertainty at the exact moment a decision is required. Because the identity-provider page is real, domain checking alone cannot answer the central question. The code represents a session. If you did not initiate that session on a device in front of you, do not authorize it. The safest response does not depend on winning a debate with the sender. It depends on moving the decision to a channel and record that existed before the new contact.
From “Personalized email” to “Cloud access”
Here, personalized email is the low-cost opening and cloud access is the high-impact destination. Reading each transition as a new capability makes the turning point visible before the story feels complete.
| Moment | What it appears to mean | What to verify |
|---|---|---|
| Personalized email | A relevant proposal or document | Was the project and sender expected? |
| Device code | A convenient way to view it | Which physical device generated this code? |
| Real sign-in page | The domain proves the request | Did you start the flow yourself? |
| Cloud access | Only the document opens | What account permissions did the session receive? |
Never enter a device code supplied by another person or message. That single boundary is more dependable than trying to judge confidence, polish or urgency.
How to interrupt cloud access
Use the following sequence as a decision aid for the short device code does not identify whose device you are authorizing, not as a test that must be completed while the sender waits.
- Never enter a device code supplied by another person or message.
- Start document access from the known project or cloud portal.
- Read the identity-provider explanation before approval.
- Report role-specific lures even when the page is legitimate.
- Use conditional-access controls for device-code flows where appropriate.
- Confirm sensitive documents with the sender through a separate channel.
Recovery after cloud access
After cloud access, recovery starts by stopping the next irreversible action. Then preserve enough context to understand how the contact moved from personalized email to a consequential change.
- Revoke sessions and tokens immediately.
- Review sign-ins for the device-code event and unfamiliar locations.
- Inspect mailbox rules and sent messages.
- Check cloud-file access around the event.
- Preserve the email and code without reusing it.
Why “Personalized email” can feel routine
In the sequence documented by Microsoft Security Research, April 6, 2026, the opening claim supplies a reason to listen. The middle step keeps the target inside the sender’s route. The final request asks for authority, money or access. None of those stages requires carelessness. The approach behind “The short device code does not identify whose device you are authorizing” works by making the next action appear consistent with the role, project or relationship already in front of the recipient.
Training often overemphasizes spelling mistakes and theatrical urgency. In this case, the stronger question is whether the process has been quietly redesigned around the new contact. “Personalized email” may look routine, yet it can position “Cloud access” as the natural conclusion. A legitimate request should remain valid after a pause, a call-back and review by another authorized person.
Four decision points before “Cloud access”
1. Personalized email
Why it works: A relevant proposal or document. In a busy day, that explanation can be enough to keep the interaction moving. The safer test is narrower: Was the project and sender expected? This does not require the recipient to prove fraud. It only requires the sender’s claim to survive contact with a record or channel that the sender did not create.
What to notice after personalized email: Observe what changes at this point in “The short device code does not identify whose device you are authorizing.” Does the sender gain a reply, a session, a payment instruction, a new device, a document, or permission to continue? Naming the capability behind a relevant proposal or document is more useful than guessing the sender’s personality. It gives a colleague or incident team a concrete fact to verify instead of a vague feeling that this particular message looked wrong.
2. Device code
Why it works: A convenient way to view it. In a busy day, that explanation can be enough to keep the interaction moving. The safer test is narrower: Which physical device generated this code? This does not require the recipient to prove fraud. It only requires the sender’s claim to survive contact with a record or channel that the sender did not create.
What to notice after device code: Observe what changes at this point in “The short device code does not identify whose device you are authorizing.” Does the sender gain a reply, a session, a payment instruction, a new device, a document, or permission to continue? Naming the capability behind a convenient way to view it is more useful than guessing the sender’s personality. It gives a colleague or incident team a concrete fact to verify instead of a vague feeling that this particular message looked wrong.
3. Real sign-in page
Why it works: The domain proves the request. In a busy day, that explanation can be enough to keep the interaction moving. The safer test is narrower: Did you start the flow yourself? This does not require the recipient to prove fraud. It only requires the sender’s claim to survive contact with a record or channel that the sender did not create.
What to notice after real sign-in page: Observe what changes at this point in “The short device code does not identify whose device you are authorizing.” Does the sender gain a reply, a session, a payment instruction, a new device, a document, or permission to continue? Naming the capability behind the domain proves the request is more useful than guessing the sender’s personality. It gives a colleague or incident team a concrete fact to verify instead of a vague feeling that this particular message looked wrong.
4. Cloud access
Why it works: Only the document opens. In a busy day, that explanation can be enough to keep the interaction moving. The safer test is narrower: What account permissions did the session receive? This does not require the recipient to prove fraud. It only requires the sender’s claim to survive contact with a record or channel that the sender did not create.
What to notice after cloud access: Observe what changes at this point in “The short device code does not identify whose device you are authorizing.” Does the sender gain a reply, a session, a payment instruction, a new device, a document, or permission to continue? Naming the capability behind only the document opens is more useful than guessing the sender’s personality. It gives a colleague or incident team a concrete fact to verify instead of a vague feeling that this particular message looked wrong.
Where identity & access needs protective friction
The first protective move is simple: Never enter a device code supplied by another person or message. The second is procedural: Start document access from the known project or cloud portal. Together, those moves separate the sender’s narrative from the organization’s evidence. They are deliberately slower than clicking Reply, but much faster than recovering money, identity access or a compromised device.
The next layer is social. Read the identity-provider explanation before approval. People bypass controls when they believe delay will disappoint a customer, executive or colleague. A good policy therefore grants explicit permission to pause and defines who owns the follow-up. The recipient should not have to investigate alone while the requester waits on the line.
Evidence to retain after “Personalized email”
Evidence about the short device code does not identify whose device you are authorizing is most useful when it captures the original route and the requested action. Do not keep chatting simply to make the sender confess. Save what already exists, note what was approved or disclosed, and move reporting to a trusted channel. The following details give responders a workable starting point:
- Revoke sessions and tokens immediately
- Review sign-ins for the device-code event and unfamiliar locations
- Inspect mailbox rules and sent messages
- Check cloud-file access around the event
A screenshot can communicate the visible story around personalized email, but the original message, full sender address, link, meeting invitation or transaction reference may contain more useful technical detail. Preserve both when it is safe to do so. Avoid forwarding suspicious material around the organization; use the approved reporting method so the artifact behind cloud access does not become a second exposure.
A two-minute response before “Cloud access”
Stop before the highest-impact request: never enter a device code supplied by another person or message. Leave the sender’s route, then check the claim in a system or contact record you already trust. If it is genuine, resume through the verified process; if it is not, report the original interaction and warn the people most likely to receive the same identity & access pretext. That sequence works even when the message is polished or the screen belongs to a legitimate service.
What identity & access teams should change
Teams should turn this case into one explicit rule and one known reporting route. The rule is: never enter a device code supplied by another person or message. The reporting route should collect the original message, channel, time and requested action without asking the employee to continue engaging.
The costume around personalized email will change with the next news cycle. The verification boundary before cloud access should not. Separate the claim from the route used to prove it, and make that consequential action wait for independent confirmation.
Microsoft Security Research, April 6, 2026 ↗
This article links to Microsoft Security Research, April 6, 2026, paraphrases its findings about the short device code does not identify whose device you are authorizing, and labels the decision framework as editorial analysis rather than presenting inferred details as observed facts.